Tech & Science
Apple Launches Manual Impersonation Risk Detection in iOS 27
Apple’s iOS 27 includes a new scam-prevention feature called Impersonation Risk Detection, which analyzes device and account data to assign risk levels—Unknown, Medium, or High—but remains disabled by default.

Apple has confirmed that iOS 27 includes a new security capability named “Impersonation Risk Detection,” designed to identify active social engineering scams in real time. The feature is not enabled automatically and must be manually activated by users.
How Impersonation Risk Detection Works
The feature targets scams where attackers impersonate banks, government agencies, or trusted individuals to pressure users into making payments or altering account information. Unlike traditional safeguards such as two-factor authentication, this tool does not rely on blocking access but instead evaluates contextual signals tied to the user’s device and Apple Account.
It returns only a risk level—Unknown, Medium, or High—to supported apps. The underlying data used in the analysis is not shared with those apps. Each app independently determines its response based on the received risk level, which may include identity verification prompts, action delays, or scam-related warnings.
Activation Steps and App Support
Users can enable Impersonation Risk Detection by navigating to Settings → Privacy & Security → Impersonation Risk Detection, then toggling on “Share with App Developers.” Apple states the feature functions exclusively within compatible applications, though it has not released a public list of supported apps.
“Unknown” indicates no suspicious activity was detected; “Medium” reflects some signs of suspicious behavior; and “High” signifies significant indicators of an ongoing scam attempt. No further technical specifications or detection thresholds have been disclosed by Apple.
Context for Real-World Scam Prevention
Globally, individuals routinely disclose sensitive financial details—including bank credentials—after receiving deceptive communications via text messages, emails, or phone calls directed at iPhone or Android devices. While iOS already includes call and message screening tools, those features cannot intervene if a user voluntarily engages with a fraudulent request.
Impersonation Risk Detection represents Apple’s first documented effort to address this gap by introducing behavioral analysis at the operating system level. Its deployment depends entirely on developer integration and user consent through the privacy setting.
Latest news
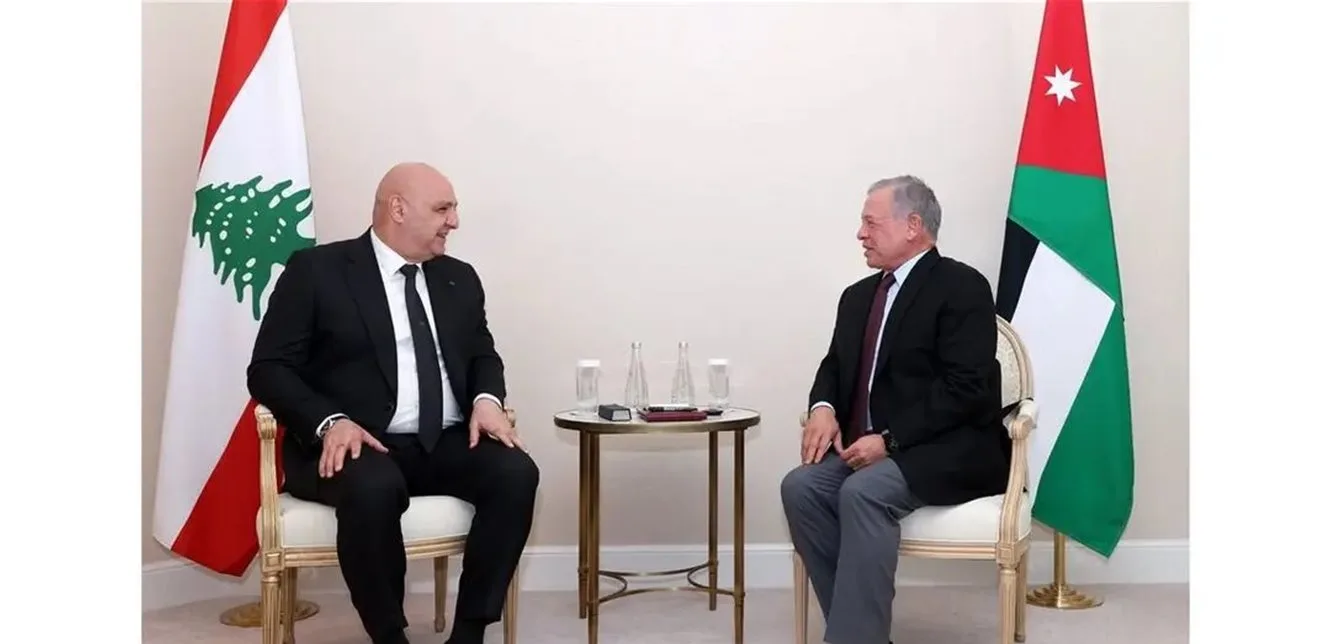
Aoun and King Abdullah Stress Stability Consolidation and End to War State

Aoun in Paris: I Follow Developments with Deep Concern
Kylie Jenner Wears Plunging Alo Sports Bra While Carrying Birkin to Gym